
Product · Security & Reliability
Security is architecture. Not a policy binder.
- In-regionData residency by architecture
- Client-ownedAzure subscription
- ISO 27001 and ISO 9001Aligned
Deployment flexibility
Your cloud by default, private when you need it.
We deploy security per engagement, not multi-tenant, not shared, not templated at the boundary.
Client-owned environment
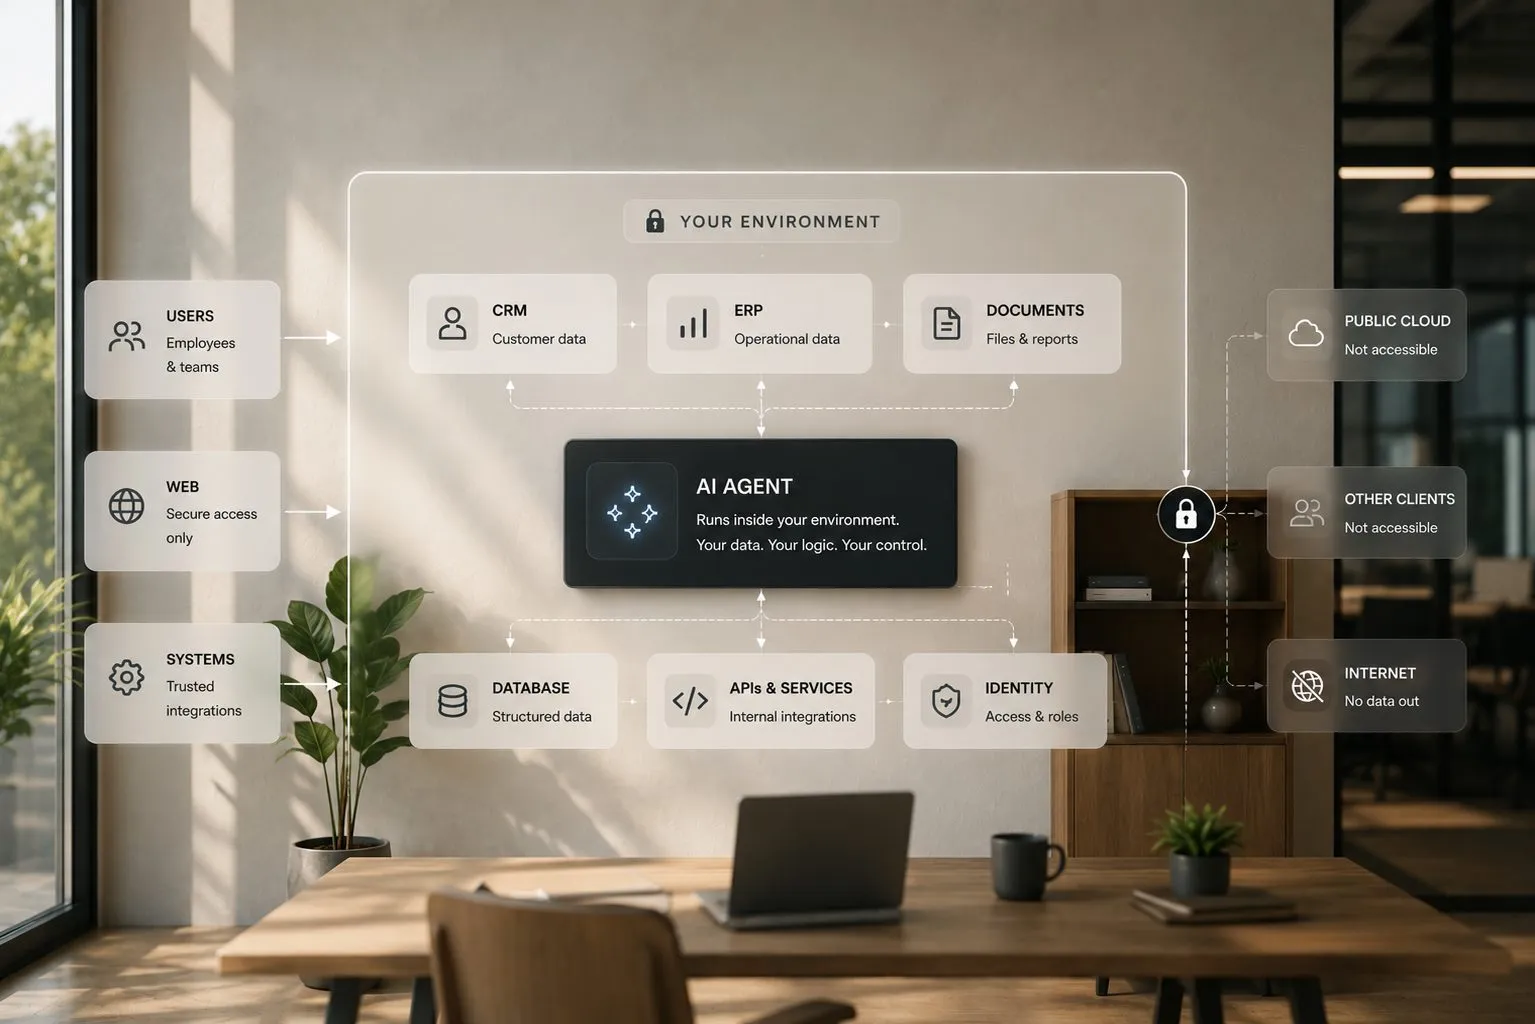
Dedicated Azure subscription per client. Segmented virtual networks, subnets separated by purpose, and a single authenticated entry point. Data, processes and business logic stay inside your environment by default.
Residency in your region
Processing and AI inference stay in the region your compliance requires: Europe for European clients, the US for US clients. Prompts and inference content stay in-region end-to-end.
On-premise and sovereign options
For elevated requirements: local servers, air-sealed setups, open-source or European models. See Technology → Sovereignty & on-premise →
Security built in, not bolted on
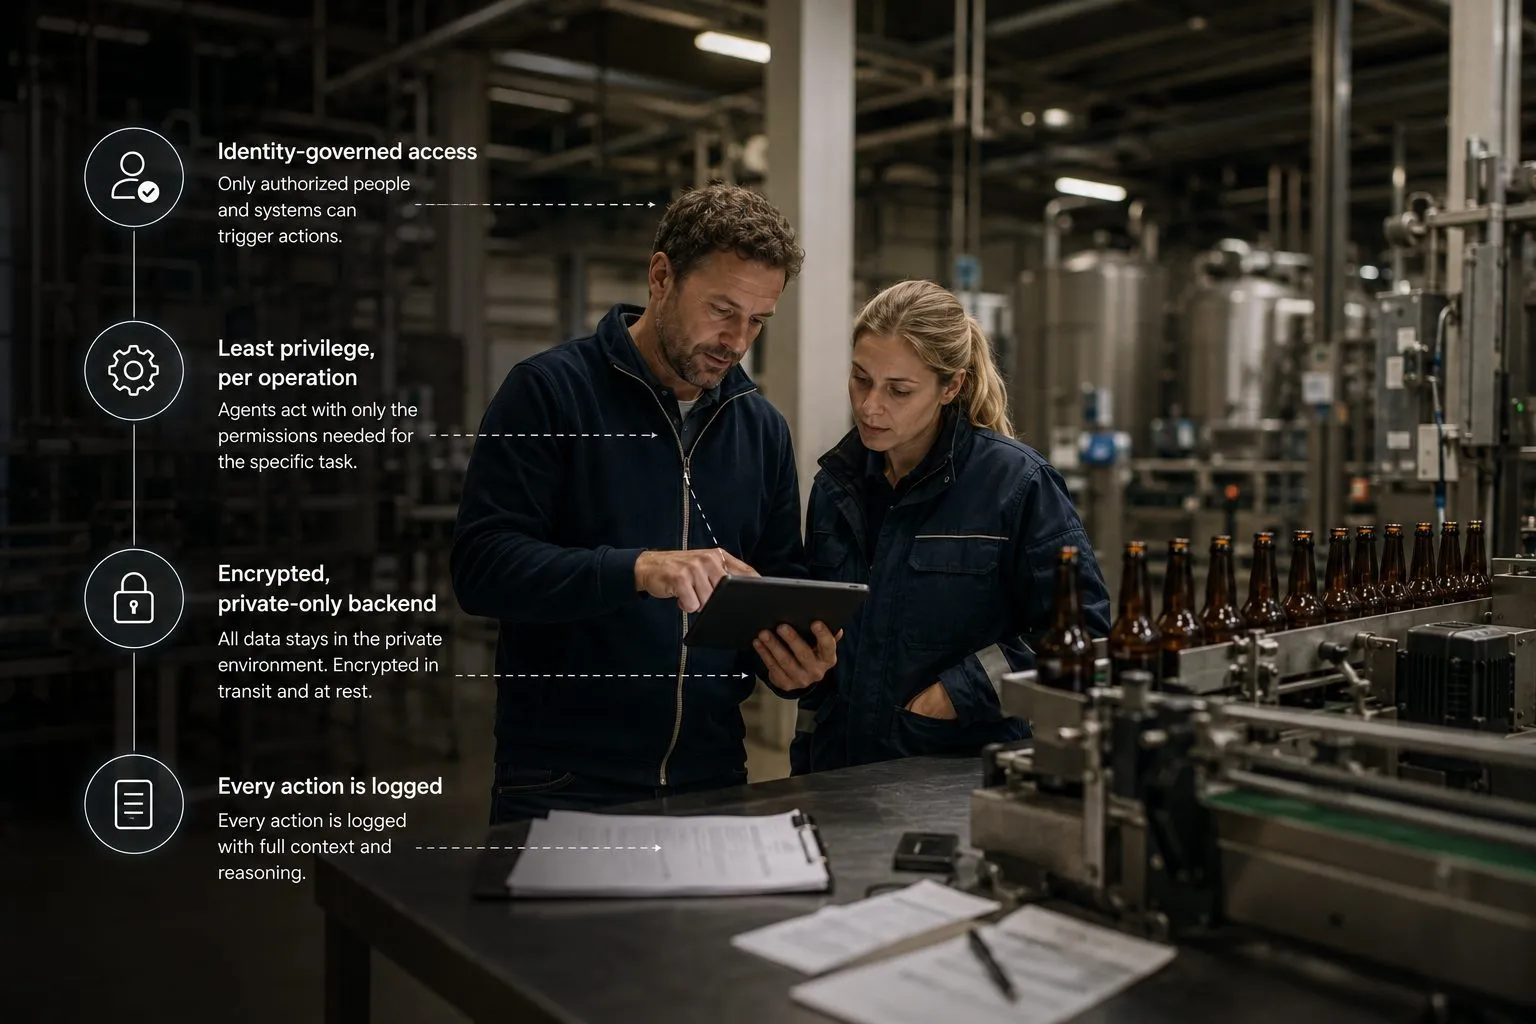
No MLM credential is stored in your environment. Access is granted by you, and revocable at any time.
Compliance
For regulated industries and markets.
GDPR
Compliant by architecture
EU AI Act
HITL on every deployment
ISO 27001 and ISO 9001
Aligned
Data residency
In-region · client-selected
Service reliability
Autonomous doesn’t mean fragile.
Infrastructure that scales
Managed container runtime with horizontal scaling per workload and isolation per agent. Not a laptop-scale deployment.
Versioned and reversible
Every agent version, configuration and adapter lives in source control. Changes go through review. Rollback is a first-class operation.
Observable and governed
Throughput, escalation rate and drift monitored from the first call, and new versions validated against the full test suite before any production traffic reaches them.
Degrades safely
If the model service is unavailable, the pipeline holds items rather than losing them. The review interface, audit log and write-back keep working.
Concrete evidence
Every deployment includes.
Security controls are agreed with your CISO in the project specification, verifiable by audit, in place from day one.
- subscription
- client_owned
- region
- client_selected · EU | US | on-premise
- identity
- entra_id · managed_identity
- key_vault
- project_scoped · backend_only
- role_based_access
- per_operation · least_privilege
- encryption_in_transit
- tls · private_backbone
- encryption_at_rest
- platform_managed
- perimeter
- single_entry_point · https_only
- data_residency
- in_region · client_selected
- audit_trail
- iso27001_aligned
Agreed with your CISO before go-live. Verifiable by audit after. Related governance controls (HITL, traceable test cases, provenance) live in Governance → Concrete evidence.
Get in touch
Talk to us and get started.
Book 30 minutes with our team. Walk us through your process. We'll show you where AI agents can make a difference.