All industries

Water treatment plant with clarifier basins seen from above

Product · Technology

The platform that runs the agents.

  • AzureNative platform
  • Two topologiesDefault · Private
  • In-regionInference and data, in your region

Our App Framework

A shared platform layer, growing with every deployment.

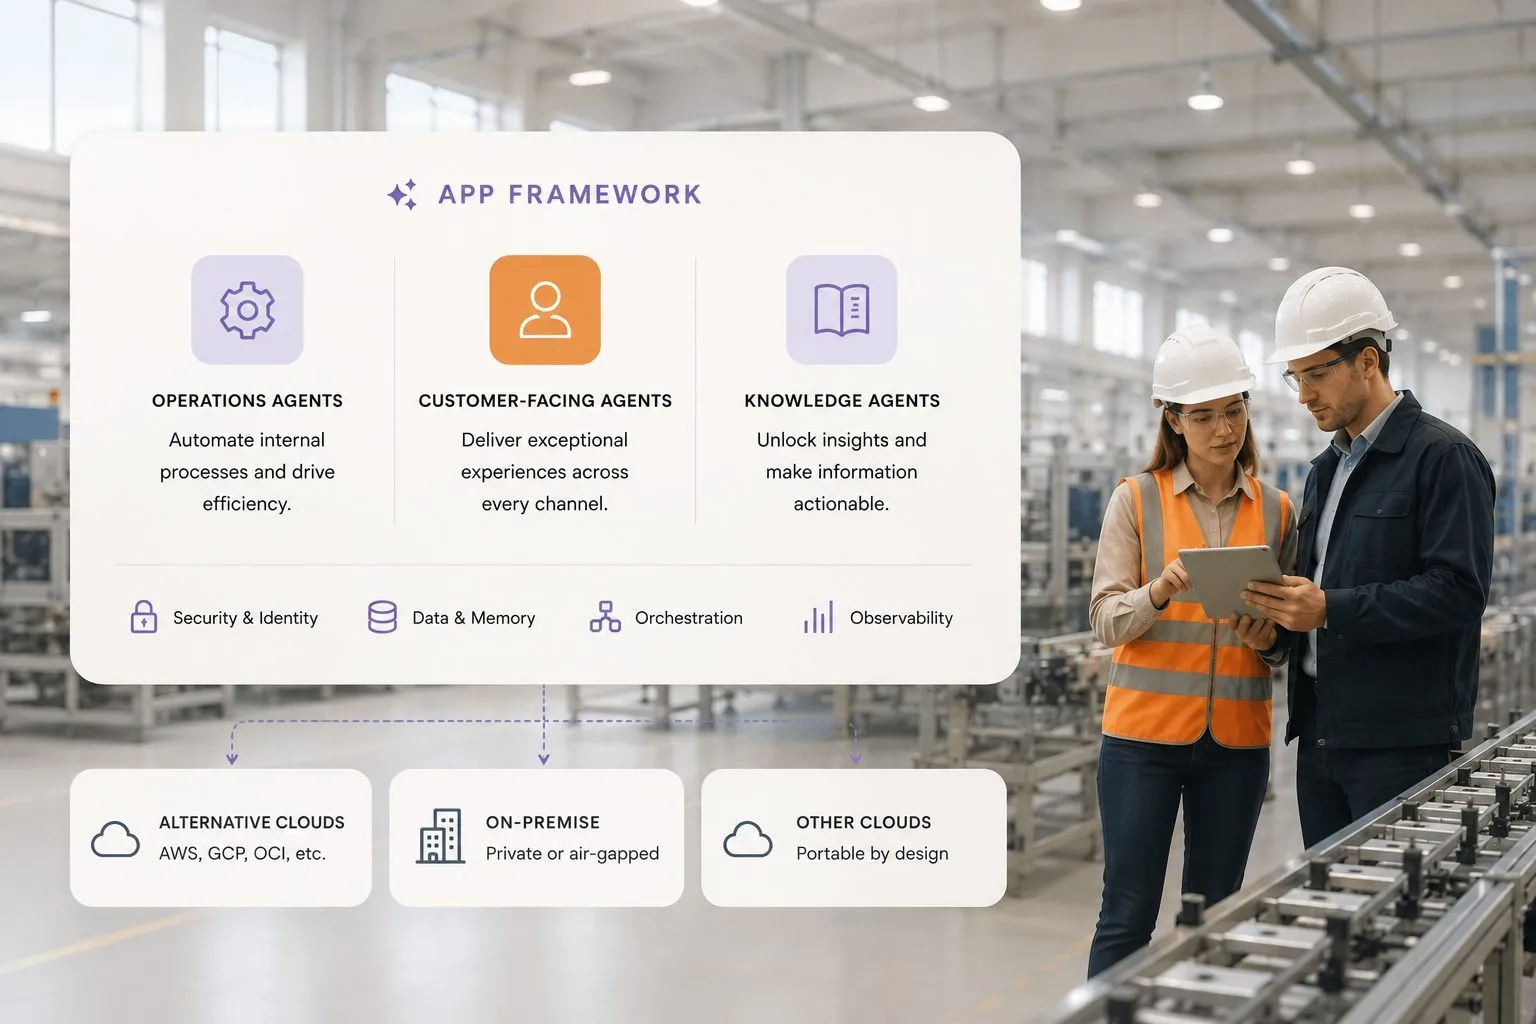
Every agent (Operations, Customer-Facing, Knowledge) is built on the same App Framework. Azure-native, not Azure-locked.

  • Security & identity

    Identity-governed everywhere: no static credentials, least privilege per operation, secrets in a project-scoped vault.

  • Data & memory

    Vector storage, structured memory, session context, inside your environment, with right-to-erasure traceable end-to-end.

  • Orchestration

    The framework runs each agent on a managed runtime, selects the best model per step, enforces HITL and approval workflows, and applies the six integration patterns per system.

  • Observability

    Decision logging, throughput metrics, escalation rates, drift monitoring, structured for operators, IT and audit.

  • Portable by design

    Deployable to on-premise, private or air-gapped environments. The platform layer is pre-built for Azure; delivery on Google Cloud or AWS is supported on request and scoped as additional engineering.

App Framework — operations, customer-facing and knowledge agents on shared security, data, orchestration and observability; portable to alternative clouds and on-premise

Two topologies

Default vs Private, chosen per engagement.

Every Machines Like Me deployment lives inside the customer’s environment. Two topology options cover the full range of enterprise security postures. The choice is a design decision at kickoff, not a product tier.

Default topology

Deployed inside a client-owned Azure subscription, with in-region inference.

Model providers
Azure OpenAI and Anthropic Claude, in your region
Infrastructure
Microsoft Azure (public)
Identity
Managed identity
Secrets
Azure Key Vault, project-scoped
Observability
Azure Monitor / Log Analytics
Data storage
Azure Storage, encrypted

Recommended where the engagement meets the regulatory baseline (EU AI Act, GDPR) without additional residency constraints.

Private topology

Deployed inside private infrastructure, on-premise or sovereign cloud.

Model providers
No public providers — self-hosted models
Infrastructure
On-premise or sovereign cloud
Identity
Managed identity, local
Secrets
Local key vault, project-scoped
Observability
Client-operated stack
Data storage
On-premise or sovereign storage, encrypted

Recommended for public sector, defense, healthcare and regulated financial services, where residency or sovereignty requirements are elevated.

Sovereignty & on-premise

Full control over your knowledge and data.

Besides our cloud-based setup, we deploy on-premise and locally hosted, for public institutions, defense, and any organization that requires complete control over its knowledge and data.

  • Local servers

    The full platform runs on your own hardware, inside your own data center, locally hosted, locally operated.

  • Sovereign model choice

    No dependency on any single model provider. Open-source and European models available where sovereignty requires it.

  • Air-sealed setups

    Air-gapped and restricted-network operation supported, nothing leaves the environment, by design.

  • Built for the public sector

    Public institutions, defense and regulated industries: deployments designed around sovereignty requirements, not adapted to them afterwards.

Reference architecture

One reference architecture. Adapted per deployment.

The same components, the same boundaries, the same control planes, adapted at the edges to your identity system, integration surface and compliance posture.

  1. 01

    Perimeter

    A single authenticated entry point over HTTPS. Application services are not exposed directly.

  2. 02

    Identity & access

    Your identity system governs every call. Least privilege by default.

  3. 03

    Data plane

    Memory and context inside your subscription, in your region.

  4. 04

    Compute plane

    Managed container runtime, isolated per agent and environment.

  5. 05

    Model plane

    In-region model hosting, providers chosen per engagement.

  6. 06

    Observability plane

    Decision logs and metrics; retention agreed per project.

  7. 07

    Integration plane

    Adapters in source control, versioned like code.

  8. 08

    Governance plane

    HITL and thresholds enforced across every plane above.

The shared platform layer is real and growing, and not every component is unified yet. Reuse reduces the scope of a project; it does not reduce it to configuration alone.

Concrete evidence

Every deployment includes.

The Technology Platform is agreed with your IT in the project specification before go-live, verifiable by audit after, in place from day one.

Technology platform · deployment declarationClient-owned
  • SubscriptionDedicated Azure subscription: client-owned, never shared.client_owned
  • TopologyDefault or Private, chosen per engagement at kickoff.default | private
  • RegionData and inference anchored to the region your compliance requires.EU · US · on-premise
  • IdentityManaged Identity through your identity system, no static credentials.✓
  • Key VaultProject-scoped secrets, backend-only access.✓
  • Model routingBest model per step, swappable at configuration time.per step
  • ObservabilityThroughput · escalation rate · drift, from the first call.✓
  • Source codeYours, licensed perpetually, in standard scope. Delivered to you at handover.perpetual

Get in touch

Talk to us and get started.

Book 30 minutes with our team. Walk us through your process. We'll show you where AI agents can make a difference.

Industry Solution Catalog

Solution Catalog

A practical overview of key processes in your sector, the challenges they involve, and the AI agent solutions that address them.